CISSP All-in-One Exam Guide (2021)
- Certified Information Systems Security Professional
- 1361 pages
- Shared February 2025
- 145 downloads
CISSP All-in-One Exam Guide (2021) ensures you are exam-ready with expert-curated content.
Preview 31 of 1361 pages
See the first 31 pages exactly as they appear in the document.
Page 1 Page 2 Page 3 Read page 3 as text
Praise for CISSP® All-in-One Exam Guide Fernando’s latest update to the CISSP All-In-One Exam Guide continues the tradition started in past collaborations with Shon Harris of breaking down key concepts and criti - cal skills in a way that prepares the reader for the exam. Once again the material proves to be not only a vital asset to exam preparation but a valued resource reference for use well after the exam has been passed. Stefanie Keuser , CISSP, Chief Information Officer, Military Officers Association of America The CISSP All-in-One Exam Guide is the only book one needs to pass the CISSP exam. Fernando Maymí is not just an author, he is a leader in the cybersecurity industry. His insight, knowledge, and expertise is reflected in the content provided in this book. The book will not only give you what you need to pass the exam, it can also be used to help you further your career in cybersecurity. Marc Coady , CISSP, Compliance Analyst, Costco Wholesale A must-have reference for any cyber security practitioner, this book provides invaluable practical knowledge on the increasingly complex universe of security concepts, controls, and best practices necessary to do business in today’s world. Steve Zalewski , Former Chief Information Security Officer, Levi Strauss & Co. Shon Harris put the CISSP certification on the map with this golden bible of the CISSP. Fernando Maymí carries that legacy forward beautifully with clarity, accuracy, and balance. I am sure that Shon would be proud. David R. Miller , CISSP, CCSP, GIAC GISP GSEC GISF, PCI QSA, LPT, ECSA, CEH, CWNA, CCNA, SME, MCT, MCIT Pro EA, MCSE: Security, CNE, Security+, etc.
Page 4 Read page 4 as text
An excellent reference. Written clearly and concisely, this book is invaluable to students, educators, and practitioners alike. Dr. Joe Adams , Founder and Executive Director, Michigan Cyber Range A lucid, enlightening, and comprehensive tour de force through the breadth of cyber security. Maymí and Harris are masters of the craft. Dr. Greg Conti , Founder, Kopidion LLC I wish I found this book earlier in my career. It certainly was the single tool I used to pass the CISSP exam, but more importantly it has taught me about security from many aspects I did not even comprehend previously. I think the knowledge that I gained from this book is going to help me in many years to come. Terrific book and resource! Janet Robinson , Chief Security Officer
Page 5 Read page 5 as text
ALL IN ONE CISSP ® E X A M G U I D E
Page 6 Read page 6 as text
ABOUT THE AUTHORS Fernando Maymí , PhD, CISSP, is a security practitioner with over 25 years’ experience in the field. He is currently Vice President of Training at IronNet Cybersecurity, where, besides develop - ing cyber talent for the company, its partners, and customers, he has led teams providing strategic consultancy, security assess - ments, red teaming, and cybersecurity exercises around the world. Previously, he led advanced research and development projects at the intersection of artificial intelligence and cybersecurity, stood up the U.S. Army’s think tank for strategic cybersecurity issues, and was a West Point faculty member for over 12 years. Fernando worked closely with Shon Harris, advising her on a multitude of projects, including the sixth edition of the CISSP All-in-One Exam Guide . Shon Harris , CISSP, was the founder and CEO of Shon Harris Security LLC and Logical Security LLC, a security consultant, a former engineer in the Air Force’s Infor - mation Warfare unit, an instructor, and an author. Shon owned and ran her own training and consulting companies for 13 years prior to her death in 2014. She consulted with Fortune 100 corporations and government agencies on extensive security issues. She authored three best-selling CISSP books, was a contributing author to Gray Hat Hacking: The Ethical Hacker’s Handbook and Security Information and Event Management (SIEM) Implementation , and a technical editor for Information Security Magazine. About the Contributor/Technical Editor Bobby E. Rogers is an information security engineer working as a contractor for Depart - ment of Defense agencies, helping to secure, certify, and accredit their information sys - tems. His duties include information system security engineering, risk management, and certification and accreditation efforts. He retired after 21 years in the U.S. Air Force, serving as a network security engineer and instructor, and has secured networks all over the world. Bobby has a master’s degree in information assurance (IA) and is pursuing a doctoral degree in cybersecurity from Capitol Technology University in Maryland. His many certifications include CISSP-ISSEP, CEH, and MCSE: Security, as well as the CompTIA A+, Network+, Security+, and Mobility+ certifications.
Page 7 Read page 7 as text
ALL IN ONE CISSP ® E X A M G U I D E Ninth Edition Fernando Maymí Shon Harris New York Chicago San Francisco Athens London Madrid Mexico City Milan New Delhi Singapore Sydney Toronto McGraw Hill is an independent entity from (ISC)²® and is not affiliated with (ISC)² in any manner. This study/training guide and/or material is not sponsored by, endorsed by, or affiliated with (ISC) 2 in any manner. This publication and accompanying media may be used in assisting students to prepare for the CISSP exam. Neither (ISC)² nor McGraw Hill warrants that use of this publication and accompanying media will ensure passing any exam. (ISC)²®, CISSP®, CAP®, ISSAP®, ISSEP®, ISSMP®, SSCP® and CBK® are trademarks or registered trademarks of (ISC)² in the United States and certain other countries. All other trademarks are trademarks of their respective owners.
Page 8 Read page 8 as text
Copyright © 2022 by McGraw Hill. All rights reserved. Except as permitted under the United States Copyright Act of 1976, no part of this publication may be reproduced or distributed in any form or by any means, or stored in a database or retrieval system, without the prior written permission of the publisher. ISBN: 978-1-26-046736-9 MHID: 1-26-046736-8 The material in this eBook also appears in the print version of this title: ISBN: 978-1-26-046737-6, MHID: 1-26-046737-6. eBook conversion by codeMantra Version 1.0 All trademarks are trademarks of their respective owners. Rather than put a trademark symbol after every occurrence of a trademarked name, we use names in an editorial fashion only, and to the benefit of the trademark owner, with no intention of infringement of the trademark. Where such designations appear in this book, they have been printed with initial caps. McGraw-Hill Education eBooks are available at special quantity discounts to use as premiums and sales promotions or for use in corporate training programs. To contact a representative, please visit the Contact Us page at www.mhprofessional.com. Information has been obtained by McGraw Hill from sources believed to be reliable. However, because of the possibility of human or mechanical error by our sources, McGraw Hill, or others, McGraw Hill does not guarantee the accuracy, adequacy, or completeness of any information and is not responsible for any errors or omissions or the results obtained from the use of such information. TERMS OF USE This is a copyrighted work and McGraw-Hill Education and its licensors reserve all rights in and to the work. Use of this work is subject to these terms. Except as permitted under the Copyright Act of 1976 and the right to store and retrieve one copy of the work, you may not decompile, disassemble, reverse engineer, reproduce, modify, create derivative works based upon, transmit, distribute, disseminate, sell, publish or sublicense the work or any part of it without McGraw-Hill Education’s prior consent. You may use the work for your own noncommercial and personal use; any other use of the work is strictly prohibited. Your right to use the work may be terminated if you fail to comply with these terms. THE WORK IS PROVIDED “AS IS.” McGRAW-HILL EDUCATION AND ITS LICENSORS MAKE NO GUARANTEES OR WARRANTIES AS TO THE ACCURACY, ADEQUACY OR COMPLETENESS OF OR RESULTS TO BE OBTAINED FROM USING THE WORK, INCLUDING ANY INFORMATION THAT CAN BE ACCESSED THROUGH THE WORK VIA HYPERLINK OR OTHERWISE, AND EXPRESSLY DISCLAIM ANY WARRANTY, EXPRESS OR IMPLIED, IN - CLUDING BUT NOT LIMITED TO IMPLIED WARRANTIES OF MERCHANTABILITY OR FITNESS FOR A PAR - TICULAR PURPOSE. McGraw-Hill Education and its licensors do not warrant or guarantee that the functions contained in the work will meet your requirements or that its operation will be uninterrupted or error free. Neither McGraw-Hill Education nor its licensors shall be liable to you or anyone else for any inaccuracy, error or omission, regardless of cause, in the work or for any damages resulting therefrom. McGraw-Hill Education has no responsibility for the content of any information ac - cessed through the work. Under no circumstances shall McGraw-Hill Education and/or its licensors be liable for any indirect, incidental, special, punitive, consequential or similar damages that result from the use of or inability to use the work, even if any of them has been advised of the possibility of such damages. This limitation of liability shall apply to any claim or cause whatsoever whether such claim or cause arises in contract, tort or otherwise.
Page 9 Read page 9 as text
We dedicate this book to all those who have served others selflessly.
Page 10 Read page 10 as text
This page intentionally left blank
Page 11 Read page 11 as text
ix CONTENTS AT A GLANCE Part I Security and Risk Management Chapter 1 Cybersecurity Governance . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3 Chapter 2 Risk Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 53 Chapter 3 Compliance . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 125 Chapter 4 Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 171 P art II Asset Security Chapter 5 Assets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 213 Chapter 6 Data Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 253 P art III Security Architecture and Engineering Chapter 7 System Architectures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 283 Chapter 8 Cryptology . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 317 Chapter 9 Security Architectures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 385 Chapter 10 Site and Facility Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 417 P art IV Communication and Network Security Chapter 11 Networking Fundamentals . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 469 Chapter 12 Wireless Networking . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 559 Chapter 13 Securing the Network . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 597 Chapter 14 Network Components . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 643 Chapter 15 Secure Communications Channels . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 681 Part V Identity and Access Management Chapter 16 Identity and Access Fundamentals . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 715 Chapter 17 Managing Identities and Access . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 765
Page 12 Read page 12 as text
CISSP All-in-One Exam Guide x P art VI Security Assessment and Testing Chapter 18 Security Assessments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 813 Chapter 19 Measuring Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 851 Part VII Security Operations Chapter 20 Managing Security Operations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 885 Chapter 21 Security Operations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 939 Chapter 22 Security Incidents . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 989 Chapter 23 Disasters . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1029 P art VIII Software Development Security Chapter 24 Software Development . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1079 Chapter 25 Secure Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1117 Appendix A Comprehensive Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1155 Appendix B Objective Map . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1209 Appendix C About the Online Content . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1225 Glossary . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 12 31 Index . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 12 53
Page 13 Read page 13 as text
xi CONTENTS From the Author . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . xxix Acknowledgments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . xxxiii Why Become a CISSP? . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . xxxv Part I Security and Risk Management Chapter 1 Cybersecurity Governance . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 3 Fundamental Cybersecurity Concepts and Terms . . . . . . . . . . . . . . 4 Confidentiality . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5 Integrity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 5 Availability . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6 Authenticity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6 Nonrepudiation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 6 Balanced Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 7 Other Security Terms . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 8 Security Governance Principles . . . . . . . . . . . . . . . . . . . . . . . . . . . . 10 Aligning Security to Business Strategy . . . . . . . . . . . . . . . . . . 13 Organizational Processes . . . . . . . . . . . . . . . . . . . . . . . . . . . . 17 Organizational Roles and Responsibilities . . . . . . . . . . . . . . . 18 Security Policies, Standards, Procedures, and Guidelines . . . . . . . . . 25 Security Policy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 27 Standards . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 29 Baselines . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 31 Guidelines . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 32 Procedures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 32 Implementation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 32 Personnel Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 33 Candidate Screening and Hiring . . . . . . . . . . . . . . . . . . . . . . 35 Employment Agreements and Policies . . . . . . . . . . . . . . . . . . 36 Onboarding, Transfers, and Termination Processes . . . . . . . . 37 Vendors, Consultants, and Contractors . . . . . . . . . . . . . . . . . 39 Compliance Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 39 Privacy Policies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 40 Security Awareness, Education, and Training Programs . . . . . . . . . . 40 Degree or Certification? . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 40 Methods and Techniques to Present Awareness and Training . . . . . . . . . . . . . . . . . . . . . . . . . . . 41
Page 14 Read page 14 as text
CISSP All-in-One Exam Guide xii Periodic Content Reviews . . . . . . . . . . . . . . . . . . . . . . . . . . . 43 Program Effectiveness Evaluation . . . . . . . . . . . . . . . . . . . . . 43 Professional Ethics . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 44 (ISC) 2 Code of Professional Ethics . . . . . . . . . . . . . . . . . . . . . 44 Organizational Code of Ethics . . . . . . . . . . . . . . . . . . . . . . . . 45 The Computer Ethics Institute . . . . . . . . . . . . . . . . . . . . . . . 45 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 46 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 46 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 48 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 51 Chapter 2 Risk Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 53 Risk Management Concepts . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 53 Holistic Risk Management . . . . . . . . . . . . . . . . . . . . . . . . . . 54 Information Systems Risk Management Policy . . . . . . . . . . . 56 The Risk Management Team . . . . . . . . . . . . . . . . . . . . . . . . . 56 The Risk Management Process . . . . . . . . . . . . . . . . . . . . . . . 57 Overview of Vulnerabilities and Threats . . . . . . . . . . . . . . . . 58 Identifying Threats and Vulnerabilities . . . . . . . . . . . . . . . . . 62 Assessing Risks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 63 Asset Valuation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 65 Risk Assessment Teams . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 66 Methodologies for Risk Assessment . . . . . . . . . . . . . . . . . . . . 67 Risk Analysis Approaches . . . . . . . . . . . . . . . . . . . . . . . . . . . 72 Qualitative Risk Analysis . . . . . . . . . . . . . . . . . . . . . . . . . . . . 76 Responding to Risks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 79 Total Risk vs. Residual Risk . . . . . . . . . . . . . . . . . . . . . . . . . . 81 Countermeasure Selection and Implementation . . . . . . . . . . 81 Types of Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 83 Control Assessments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 88 Monitoring Risks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 91 Effectiveness Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . 91 Change Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 92 Compliance Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . 93 Risk Reporting . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 94 Continuous Improvement . . . . . . . . . . . . . . . . . . . . . . . . . . . 95 Supply Chain Risk Management . . . . . . . . . . . . . . . . . . . . . . . . . . . 96 Upstream and Downstream Suppliers . . . . . . . . . . . . . . . . . . 98 Risks Associated with Hardware, Software, and Services . . . . . 98 Other Third-Party Risks . . . . . . . . . . . . . . . . . . . . . . . . . . . . 99 Minimum Security Requirements . . . . . . . . . . . . . . . . . . . . . 100 Service Level Agreements . . . . . . . . . . . . . . . . . . . . . . . . . . . . 101 Business Continuity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 101 Standards and Best Practices . . . . . . . . . . . . . . . . . . . . . . . . . 104 Making BCM Part of the Enterprise Security Program . . . . . 106 Business Impact Analysis . . . . . . . . . . . . . . . . . . . . . . . . . . . . 108
Page 15 Read page 15 as text
Contents xiii Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 116 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 116 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 118 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 121 Chapter 3 Compliance . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 125 Laws and Regulations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 125 Types of Legal Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 126 Common Law Revisited . . . . . . . . . . . . . . . . . . . . . . . . . . . . 129 Cybercrimes and Data Breaches . . . . . . . . . . . . . . . . . . . . . . . . . . . 130 Complexities in Cybercrime . . . . . . . . . . . . . . . . . . . . . . . . . 132 The Evolution of Attacks . . . . . . . . . . . . . . . . . . . . . . . . . . . . 134 International Issues . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 138 Data Breaches . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 139 Import/Export Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . . 145 Transborder Data Flow . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 146 Privacy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 147 Licensing and Intellectual Property Requirements . . . . . . . . . . . . . . 147 Trade Secret . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 148 Copyright . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 149 Trademark . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 150 Patent . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 151 Internal Protection of Intellectual Property . . . . . . . . . . . . . . 152 Software Piracy . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 153 Compliance Requirements . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 155 Contractual, Legal, Industry Standards, and Regulatory Requirements . . . . . . . . . . . . . . . . . . . . . . 156 Privacy Requirements . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 158 Liability and Its Ramifications . . . . . . . . . . . . . . . . . . . . . . . . 158 Requirements for Investigations . . . . . . . . . . . . . . . . . . . . . . . . . . . 161 Administrative . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 161 Criminal . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 162 Civil . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 162 Regulatory . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 162 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 162 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 163 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 165 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 168 Chapter 4 Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 171 Overview of Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 171 Risk Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 173 NIST RMF . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 173 ISO/IEC 27005 . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 177 OCTAVE . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 178 FAIR . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 179
Page 16 Read page 16 as text
CISSP All-in-One Exam Guide xiv Information Security Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . 179 Security Program Frameworks . . . . . . . . . . . . . . . . . . . . . . . . 180 Security Control Frameworks . . . . . . . . . . . . . . . . . . . . . . . . 183 Enterprise Architecture Frameworks . . . . . . . . . . . . . . . . . . . . . . . . 189 Why Do We Need Enterprise Architecture Frameworks? . . . . 191 Zachman Framework . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 192 The Open Group Architecture Framework . . . . . . . . . . . . . . 194 Military-Oriented Architecture Frameworks . . . . . . . . . . . . . 195 Other Frameworks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 196 ITIL . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 196 Six Sigma . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 197 Capability Maturity Model . . . . . . . . . . . . . . . . . . . . . . . . . . 197 Putting It All Together . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 199 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 203 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 203 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 205 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 208 P art II Asset Security Chapter 5 Assets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 213 Information and Assets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 214 Identification . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 214 Classification . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 215 Physical Security Considerations . . . . . . . . . . . . . . . . . . . . . . . . . . . 220 Protecting Mobile Devices . . . . . . . . . . . . . . . . . . . . . . . . . . . 220 Paper Records . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 221 Safes . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 221 Managing the Life Cycle of Assets . . . . . . . . . . . . . . . . . . . . . . . . . . 222 Ownership . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 223 Inventories . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 224 Secure Provisioning . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 227 Asset Retention . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 228 Data Life Cycle . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 230 Data Acquisition . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 230 Data Storage . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 232 Data Use . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 237 Data Sharing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 238 Data Archival . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 239 Data Destruction . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 240 Data Roles . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 244 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 245 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 245 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 247 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 250
Page 17 Read page 17 as text
Contents xv Chapter 6 Data Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 253 Data Security Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 253 Data States . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 254 Standards . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 258 Scoping and Tailoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 258 Data Protection Methods . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 258 Digital Asset Management . . . . . . . . . . . . . . . . . . . . . . . . . . . 261 Digital Rights Management . . . . . . . . . . . . . . . . . . . . . . . . . . 263 Data Loss Prevention . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 265 Cloud Access Security Broker . . . . . . . . . . . . . . . . . . . . . . . . 275 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 276 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 276 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 277 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 279 P art III Security Architecture and Engineering Chapter 7 System Architectures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 283 General System Architectures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 283 Client-Based Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 284 Server-Based Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 284 Database Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 285 High-Performance Computing Systems . . . . . . . . . . . . . . . . . 288 Industrial Control Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 289 Devices . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 291 Distributed Control System . . . . . . . . . . . . . . . . . . . . . . . . . . 293 Supervisory Control and Data Acquisition . . . . . . . . . . . . . . 294 ICS Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 294 Virtualized Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 296 Virtual Machines . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 296 Containerization . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 298 Microservices . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 299 Serverless . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 299 Cloud-Based Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 301 Software as a Service . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 302 Platform as a Service . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 303 Infrastructure as a Service . . . . . . . . . . . . . . . . . . . . . . . . . . . 304 Everything as a Service . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 304 Cloud Deployment Models . . . . . . . . . . . . . . . . . . . . . . . . . . 305 Pervasive Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 305 Embedded Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 306 Internet of Things . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 306 Distributed Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 307 Edge Computing Systems . . . . . . . . . . . . . . . . . . . . . . . . . . . 308
Page 18 Read page 18 as text
CISSP All-in-One Exam Guide xvi Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 310 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 310 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 311 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 314 Chapter 8 Cryptology . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 317 The History of Cryptography . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 317 Cryptography Definitions and Concepts . . . . . . . . . . . . . . . . . . . . . 321 Cryptosystems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 323 Kerckhoffs’ Principle . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 324 The Strength of the Cryptosystem . . . . . . . . . . . . . . . . . . . . . 325 One-Time Pad . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 325 Cryptographic Life Cycle . . . . . . . . . . . . . . . . . . . . . . . . . . . . 328 Cryptographic Methods . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 328 Symmetric Key Cryptography . . . . . . . . . . . . . . . . . . . . . . . . 329 Asymmetric Key Cryptography . . . . . . . . . . . . . . . . . . . . . . . 335 Elliptic Curve Cryptography . . . . . . . . . . . . . . . . . . . . . . . . . 342 Quantum Cryptography . . . . . . . . . . . . . . . . . . . . . . . . . . . . 344 Hybrid Encryption Methods . . . . . . . . . . . . . . . . . . . . . . . . . 346 Integrity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 351 Hashing Functions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 351 Message Integrity Verification . . . . . . . . . . . . . . . . . . . . . . . . 354 Public Key Infrastructure . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 359 Digital Certificates . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 359 Certificate Authorities . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 360 Registration Authorities . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 362 PKI Steps . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 362 Key Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 364 Attacks Against Cryptography . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 367 Key and Algorithm Attacks . . . . . . . . . . . . . . . . . . . . . . . . . . 367 Implementation Attacks . . . . . . . . . . . . . . . . . . . . . . . . . . . . 370 Other Attacks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 372 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 375 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 376 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 379 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 381 Chapter 9 Security Architectures . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 385 Threat Modeling . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 385 Attack Trees . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 386 STRIDE . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 387 The Lockheed Martin Cyber Kill Chain . . . . . . . . . . . . . . . . 387 The MITRE ATT&CK Framework . . . . . . . . . . . . . . . . . . . 389 Why Bother with Threat Modeling . . . . . . . . . . . . . . . . . . . . 389
Page 19 Read page 19 as text
Contents xvii Secure Design Principles . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 390 Defense in Depth . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 390 Zero Trust . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 392 Trust But Verify . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 392 Shared Responsibility . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 392 Separation of Duties . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 393 Least Privilege . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 394 Keep It Simple . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 395 Secure Defaults . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 396 Fail Securely . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 396 Privacy by Design . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 397 Security Models . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 397 Bell-LaPadula Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 398 Biba Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 399 Clark-Wilson Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 400 Noninterference Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 400 Brewer and Nash Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . 402 Graham-Denning Model . . . . . . . . . . . . . . . . . . . . . . . . . . . . 402 Harrison-Ruzzo-Ullman Model . . . . . . . . . . . . . . . . . . . . . . . 402 Security Requirements . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 404 Security Capabilities of Information Systems . . . . . . . . . . . . . . . . . 404 Trusted Platform Module . . . . . . . . . . . . . . . . . . . . . . . . . . . 404 Hardware Security Module . . . . . . . . . . . . . . . . . . . . . . . . . . 406 Self-Encrypting Drive . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 407 Bus Encryption . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 407 Secure Processing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 408 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 411 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 412 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 413 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 415 Chapter 10 Site and Facility Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 417 Site and Facility Design . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 417 Security Principles . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 418 The Site Planning Process . . . . . . . . . . . . . . . . . . . . . . . . . . . 423 Crime Prevention Through Environmental Design . . . . . . . . 427 Designing a Physical Security Program . . . . . . . . . . . . . . . . . 433 Site and Facility Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 441 Work Area Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 441 Data Processing Facilities . . . . . . . . . . . . . . . . . . . . . . . . . . . . 443 Distribution Facilities . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 446 Storage Facilities . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 447 Utilities . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 448 Fire Safety . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 454 Environmental Issues . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 461
Page 20 Read page 20 as text
CISSP All-in-One Exam Guide xviii Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 461 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 461 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 463 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 465 P art IV Communication and Network Security Chapter 11 Networking Fundamentals . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 469 Data Communications Foundations . . . . . . . . . . . . . . . . . . . . . . . . 469 Network Reference Models . . . . . . . . . . . . . . . . . . . . . . . . . . 470 Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 471 Application Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 474 Presentation Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 475 Session Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 477 Transport Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 479 Network Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 480 Data Link Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 480 Physical Layer . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 483 Functions and Protocols in the OSI Model . . . . . . . . . . . . . . 483 Tying the Layers Together . . . . . . . . . . . . . . . . . . . . . . . . . . . 485 Local Area Networks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 487 Network Topology . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 487 Medium Access Control Mechanisms . . . . . . . . . . . . . . . . . . 489 Layer 2 Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 494 Transmission Methods . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 499 Layer 2 Security Standards . . . . . . . . . . . . . . . . . . . . . . . . . . . 500 Internet Protocol Networking . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 502 TCP . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 503 IP Addressing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 510 IPv6 . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 512 Address Resolution Protocol . . . . . . . . . . . . . . . . . . . . . . . . . 515 Dynamic Host Configuration Protocol . . . . . . . . . . . . . . . . . 517 Internet Control Message Protocol . . . . . . . . . . . . . . . . . . . . 520 Simple Network Management Protocol . . . . . . . . . . . . . . . . . 522 Domain Name Service . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 524 Network Address Translation . . . . . . . . . . . . . . . . . . . . . . . . . 531 Routing Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 533 Intranets and Extranets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 537 Metropolitan Area Networks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 538 Metro Ethernet . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 539 Wide Area Networks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 540 Dedicated Links . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 541 WAN Technologies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 543
Page 21 Read page 21 as text
Contents xix Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 552 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 553 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 555 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 557 Chapter 12 Wireless Networking . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 559 Wireless Communications Techniques . . . . . . . . . . . . . . . . . . . . . . 559 Spread Spectrum . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 561 Orthogonal Frequency Division Multiplexing . . . . . . . . . . . . 563 Wireless Networking Fundamentals . . . . . . . . . . . . . . . . . . . . . . . . 564 WLAN Components . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 564 WLAN Standards . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 565 Other Wireless Network Standards . . . . . . . . . . . . . . . . . . . . 568 Other Important Standards . . . . . . . . . . . . . . . . . . . . . . . . . . 573 Evolution of WLAN Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 574 802.11 . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 575 802.11i . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 576 802.11w . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 578 WPA3 . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 578 802.1X . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 579 Best Practices for Securing WLANs . . . . . . . . . . . . . . . . . . . . . . . . . 582 Mobile Wireless Communication . . . . . . . . . . . . . . . . . . . . . . . . . . 582 Multiple Access Technologies . . . . . . . . . . . . . . . . . . . . . . . . . 584 Generations of Mobile Wireless . . . . . . . . . . . . . . . . . . . . . . . 585 Satellites . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 588 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 590 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 590 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 592 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 594 Chapter 13 Securing the Network . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 597 Applying Secure Design Principles to Network Architectures . . . . . 597 Secure Networking . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 599 Link Encryption vs. End-to-End Encryption . . . . . . . . . . . . . 600 TLS . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 602 VPN . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 605 Secure Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 611 Web Services . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 611 Domain Name System . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 616 Electronic Mail . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 621 Multilayer Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 626 Distributed Network Protocol 3 . . . . . . . . . . . . . . . . . . . . . . 626 Controller Area Network Bus . . . . . . . . . . . . . . . . . . . . . . . . 627 Modbus . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 627
Page 22 Read page 22 as text
CISSP All-in-One Exam Guide xx Converged Protocols . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 627 Encapsulation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 628 Fiber Channel over Ethernet . . . . . . . . . . . . . . . . . . . . . . . . . 628 Internet Small Computer Systems Interface . . . . . . . . . . . . . . 629 Network Segmentation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 629 VLANs . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 630 Virtual eXtensible Local Area Network . . . . . . . . . . . . . . . . . 632 Software-Defined Networks . . . . . . . . . . . . . . . . . . . . . . . . . . 632 Software-Defined Wide Area Network . . . . . . . . . . . . . . . . . 635 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 635 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 636 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 638 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 640 Chapter 14 Network Components . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 643 Transmission Media . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 643 Types of Transmission . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 644 Cabling . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 648 Bandwidth and Throughput . . . . . . . . . . . . . . . . . . . . . . . . . 654 Network Devices . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 655 Repeaters . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 655 Bridges . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 656 Switches . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 657 Routers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 660 Gateways . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 662 Proxy Servers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 663 PBXs . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 665 Network Access Control Devices . . . . . . . . . . . . . . . . . . . . . . 667 Network Diagramming . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 668 Operation of Hardware . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 670 Endpoint Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 673 Content Distribution Networks . . . . . . . . . . . . . . . . . . . . . . . . . . . 674 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 674 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 675 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 677 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 678 Chapter 15 Secure Communications Channels . . . . . . . . . . . . . . . . . . . . . . . . . . . 681 Voice Communications . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 682 Public Switched Telephone Network . . . . . . . . . . . . . . . . . . . 682 DSL . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 683 ISDN . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 685 Cable Modems . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 686 IP Telephony . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 687
Page 23 Read page 23 as text
Contents xxi Multimedia Collaboration . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 693 Meeting Applications . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 694 Unified Communications . . . . . . . . . . . . . . . . . . . . . . . . . . . 695 Remote Access . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 696 VPN . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 697 Desktop Virtualization . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 699 Secure Shell . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 701 Data Communications . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 702 Network Sockets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 703 Remote Procedure Calls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 703 Virtualized Networks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 704 Third-Party Connectivity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 705 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 707 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 707 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 709 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 711 Part V Identity and Access Management Chapter 16 Identity and Access Fundamentals . . . . . . . . . . . . . . . . . . . . . . . . . . . 715 Identification, Authentication, Authorization, and Accountability . . . . 715 Identification and Authentication . . . . . . . . . . . . . . . . . . . . . 718 Knowledge-Based Authentication . . . . . . . . . . . . . . . . . . . . . 720 Biometric Authentication . . . . . . . . . . . . . . . . . . . . . . . . . . . 723 Ownership-Based Authentication . . . . . . . . . . . . . . . . . . . . . 729 Credential Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 736 Password Managers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 736 Password Synchronization . . . . . . . . . . . . . . . . . . . . . . . . . . . 737 Self-Service Password Reset . . . . . . . . . . . . . . . . . . . . . . . . . . 737 Assisted Password Reset . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 738 Just-in-Time Access . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 738 Registration and Proofing of Identity . . . . . . . . . . . . . . . . . . . 738 Profile Update . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 740 Session Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 740 Accountability . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 741 Identity Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 745 Directory Services . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 747 Directories’ Role in Identity Management . . . . . . . . . . . . . . . 748 Single Sign-On . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 750 Federated Identity Management . . . . . . . . . . . . . . . . . . . . . . 752 Federated Identity with a Third-Party Service . . . . . . . . . . . . . . . . . 754 Integration Issues . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 754 On-Premise . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 755 Cloud . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 756 Hybrid . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 756
Page 24 Read page 24 as text
CISSP All-in-One Exam Guide xxii Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 756 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 757 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 759 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 762 Chapter 17 Managing Identities and Access . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 765 Authorization Mechanisms . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 765 Discretionary Access Control . . . . . . . . . . . . . . . . . . . . . . . . . 766 Mandatory Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . 768 Role-Based Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . 771 Rule-Based Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . 774 Attribute-Based Access Control . . . . . . . . . . . . . . . . . . . . . . . 774 Risk-Based Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . . 775 Implementing Authentication and Authorization Systems . . . . . . . . 776 Access Control and Markup Languages . . . . . . . . . . . . . . . . . 776 OAuth . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 782 OpenID Connect . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 783 Kerberos . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 784 Remote Access Control Technologies . . . . . . . . . . . . . . . . . . . 789 Managing the Identity and Access Provisioning Life Cycle . . . . . . . 795 Provisioning . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 796 Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 796 Compliance . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 796 Configuration Management . . . . . . . . . . . . . . . . . . . . . . . . . 799 Deprovisioning . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 800 Controlling Physical and Logical Access . . . . . . . . . . . . . . . . . . . . . 801 Information Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . 801 System and Application Access Control . . . . . . . . . . . . . . . . . 802 Access Control to Devices . . . . . . . . . . . . . . . . . . . . . . . . . . . 802 Facilities Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . . . 802 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 804 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 804 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 805 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 808 P art VI Security Assessment and Testing Chapter 18 Security Assessments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 813 Test, Assessment, and Audit Strategies . . . . . . . . . . . . . . . . . . . . . . . 813 Designing an Assessment . . . . . . . . . . . . . . . . . . . . . . . . . . . . 814 Validating an Assessment . . . . . . . . . . . . . . . . . . . . . . . . . . . . 815 Testing Technical Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 817 Vulnerability Testing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 817 Other Vulnerability Types . . . . . . . . . . . . . . . . . . . . . . . . . . . 819 Penetration Testing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 822 Red Teaming . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 827
Page 25 Read page 25 as text
Contents xxiii Breach Attack Simulations . . . . . . . . . . . . . . . . . . . . . . . . . . . 828 Log Reviews . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 828 Synthetic Transactions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 832 Code Reviews . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 833 Code Testing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 834 Misuse Case Testing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 835 Test Coverage . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 837 Interface Testing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 837 Compliance Checks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 838 Conducting Security Audits . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 838 Internal Audits . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 840 External Audits . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 842 Third-Party Audits . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 843 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 844 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 845 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 846 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 848 Chapter 19 Measuring Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 851 Quantifying Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 851 Security Metrics . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 853 Key Performance and Risk Indicators . . . . . . . . . . . . . . . . . . 855 Security Process Data . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 857 Account Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 858 Backup Verification . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 860 Security Training and Security Awareness Training . . . . . . . . 863 Disaster Recovery and Business Continuity . . . . . . . . . . . . . . 867 Reporting . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 869 Analyzing Results . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 870 Writing Technical Reports . . . . . . . . . . . . . . . . . . . . . . . . . . . 872 Executive Summaries . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 873 Management Review and Approval . . . . . . . . . . . . . . . . . . . . . . . . . 875 Before the Management Review . . . . . . . . . . . . . . . . . . . . . . 876 Reviewing Inputs . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 876 Management Approval . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 877 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 877 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 878 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 879 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 881 Part VII Security Operations Chapter 20 Managing Security Operations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 885 Foundational Security Operations Concepts . . . . . . . . . . . . . . . . . . 885 Accountability . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 887 Need-to-Know/Least Privilege . . . . . . . . . . . . . . . . . . . . . . . . 888
Page 26 Read page 26 as text
CISSP All-in-One Exam Guide xxiv Separation of Duties and Responsibilities . . . . . . . . . . . . . . . 888 Privileged Account Management . . . . . . . . . . . . . . . . . . . . . . 889 Job Rotation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 889 Service Level Agreements . . . . . . . . . . . . . . . . . . . . . . . . . . . . 890 Change Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 891 Change Management Practices . . . . . . . . . . . . . . . . . . . . . . . 891 Change Management Documentation . . . . . . . . . . . . . . . . . . 893 Configuration Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 893 Baselining . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 894 Provisioning . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 894 Automation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 895 Resource Protection . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 895 System Images . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 896 Source Files . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 896 Backups . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 896 Vulnerability and Patch Management . . . . . . . . . . . . . . . . . . . . . . . 900 Vulnerability Management . . . . . . . . . . . . . . . . . . . . . . . . . . 900 Patch Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 903 Physical Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 906 External Perimeter Security Controls . . . . . . . . . . . . . . . . . . . 906 Facility Access Control . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 916 Internal Security Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . 924 Personnel Access Controls . . . . . . . . . . . . . . . . . . . . . . . . . . . 924 Intrusion Detection Systems . . . . . . . . . . . . . . . . . . . . . . . . . 925 Auditing Physical Access . . . . . . . . . . . . . . . . . . . . . . . . . . . . 929 Personnel Safety and Security . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 929 Travel . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 930 Security Training and Awareness . . . . . . . . . . . . . . . . . . . . . . 930 Emergency Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . 931 Duress . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 931 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 932 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 932 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 934 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 937 Chapter 21 Security Operations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 939 The Security Operations Center . . . . . . . . . . . . . . . . . . . . . . . . . . . 939 Elements of a Mature SOC . . . . . . . . . . . . . . . . . . . . . . . . . . 940 Threat Intelligence . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 941 Preventive and Detective Measures . . . . . . . . . . . . . . . . . . . . . . . . . 944 Firewalls . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 945 Intrusion Detection and Prevention Systems . . . . . . . . . . . . . 967 Antimalware Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 969 Sandboxing . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 972 Outsourced Security Services . . . . . . . . . . . . . . . . . . . . . . . . . 973 Honeypots and Honeynets . . . . . . . . . . . . . . . . . . . . . . . . . . 974 Artificial Intelligence Tools . . . . . . . . . . . . . . . . . . . . . . . . . . 976
Page 27 Read page 27 as text
Contents xxv Logging and Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 978 Log Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 978 Security Information and Event Management . . . . . . . . . . . . 979 Egress Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 981 User and Entity Behavior Analytics . . . . . . . . . . . . . . . . . . . . 981 Continuous Monitoring . . . . . . . . . . . . . . . . . . . . . . . . . . . . 981 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 982 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 983 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 984 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 986 Chapter 22 Security Incidents . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 989 Overview of Incident Management . . . . . . . . . . . . . . . . . . . . . . . . . 989 Detection . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 995 Response . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 996 Mitigation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 996 Reporting . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 997 Recovery . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 998 Remediation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 999 Lessons Learned . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 999 Incident Response Planning . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1000 Roles and Responsibilities . . . . . . . . . . . . . . . . . . . . . . . . . . . 1000 Incident Classification . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1002 Notifications . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1003 Operational Tasks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1004 Runbooks . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1006 Investigations . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1006 Motive, Opportunity, and Means . . . . . . . . . . . . . . . . . . . . . 1007 Computer Criminal Behavior . . . . . . . . . . . . . . . . . . . . . . . . 1008 Evidence Collection and Handling . . . . . . . . . . . . . . . . . . . . 1008 What Is Admissible in Court? . . . . . . . . . . . . . . . . . . . . . . . . 1013 Digital Forensics Tools, Tactics, and Procedures . . . . . . . . . . . 1015 Forensic Investigation Techniques . . . . . . . . . . . . . . . . . . . . . 1016 Other Investigative Techniques . . . . . . . . . . . . . . . . . . . . . . . 1018 Forensic Artifacts . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1020 Reporting and Documenting . . . . . . . . . . . . . . . . . . . . . . . . . 1021 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1022 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1022 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1024 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1026 Chapter 23 Disasters . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1029 Recovery Strategies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1029 Business Process Recovery . . . . . . . . . . . . . . . . . . . . . . . . . . . 1033 Data Backup . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1034 Documentation . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1041 Human Resources . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1042
Page 28 Read page 28 as text
CISSP All-in-One Exam Guide xxvi Recovery Site Strategies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1043 Availability . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1049 Disaster Recovery Processes . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1053 Response . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1055 Personnel . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1055 Communications . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1056 Assessment . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1058 Restoration . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1058 Training and Awareness . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1060 Lessons Learned . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1061 Testing Disaster Recovery Plans . . . . . . . . . . . . . . . . . . . . . . . 1061 Business Continuity . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1065 BCP Life Cycle . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1065 Information Systems Availability . . . . . . . . . . . . . . . . . . . . . . 1067 End-User Environment . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1071 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1071 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1072 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1073 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1075 P art VIII Software Development Security Chapter 24 Software Development . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1079 Software Development Life Cycle . . . . . . . . . . . . . . . . . . . . . . . . . . 1079 Project Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1081 Requirements Gathering Phase . . . . . . . . . . . . . . . . . . . . . . . 1082 Design Phase . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1083 Development Phase . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1087 Testing Phase . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1089 Operations and Maintenance Phase . . . . . . . . . . . . . . . . . . . . 1091 Development Methodologies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1095 Waterfall Methodology . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1095 Prototyping . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1096 Incremental Methodology . . . . . . . . . . . . . . . . . . . . . . . . . . . 1096 Spiral Methodology . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1098 Rapid Application Development . . . . . . . . . . . . . . . . . . . . . . 1099 Agile Methodologies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1100 DevOps . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1103 DevSecOps . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1104 Other Methodologies . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1104 Maturity Models . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1106 Capability Maturity Model Integration . . . . . . . . . . . . . . . . . 1107 Software Assurance Maturity Model . . . . . . . . . . . . . . . . . . . 1109
Page 29 Read page 29 as text
Contents xxvii Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1110 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1110 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1112 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1114 Chapter 25 Secure Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1117 Programming Languages and Concepts . . . . . . . . . . . . . . . . . . . . . . 1118 Assemblers, Compilers, Interpreters . . . . . . . . . . . . . . . . . . . . 1120 Runtime Environments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1122 Object-Oriented Programming Concepts . . . . . . . . . . . . . . . 1124 Cohesion and Coupling . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1130 Application Programming Interfaces . . . . . . . . . . . . . . . . . . . 1132 Software Libraries . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1132 Secure Software Development . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1133 Source Code Vulnerabilities . . . . . . . . . . . . . . . . . . . . . . . . . . 1133 Secure Coding Practices . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1134 Security Controls for Software Development . . . . . . . . . . . . . . . . . 1136 Development Platforms . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1137 Tool Sets . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1138 Application Security Testing . . . . . . . . . . . . . . . . . . . . . . . . . 1139 Continuous Integration and Delivery . . . . . . . . . . . . . . . . . . 1140 Security Orchestration, Automation, and Response . . . . . . . . 1141 Software Configuration Management . . . . . . . . . . . . . . . . . . 1142 Code Repositories . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1143 Software Security Assessments . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1144 Risk Analysis and Mitigation . . . . . . . . . . . . . . . . . . . . . . . . . 1144 Change Management . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1145 Assessing the Security of Acquired Software . . . . . . . . . . . . . . . . . . 1145 Commercial Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1146 Open-Source Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1146 Third-Party Software . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1147 Managed Services . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1148 Chapter Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1148 Quick Review . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1148 Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1150 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1152 Appendix A Comprehensive Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1155 Answers . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1189 Appendix B Objective Map . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1209 Appendix C About the Online Content . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1225 System Requirements . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1225 Your Total Seminars Training Hub Account . . . . . . . . . . . . . . . . . . 1225 Privacy Notice . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1225
Page 30 Read page 30 as text
CISSP All-in-One Exam Guide xxviii Single User License Terms and Conditions . . . . . . . . . . . . . . . . . . . 1225 TotalTester Online . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1227 Graphical Questions . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1227 Online Flash Cards . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1228 Single User License Terms and Conditions . . . . . . . . . . . . . . 1228 Technical Support . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 1229 Glossary . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 12 31 Index . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . . 12 53
Page 31 Read page 31 as text
xxix FROM THE AUTHOR Thank you for investing your resources in this ninth edition of the CISSP All-in-One Exam Guide . I am confident you’ll find it helpful, not only as you prepare for the CISSP exam, but as a reference in your future professional endeavors. That was one of the over - arching goals of Shon Harris when she wrote the first six editions and is something I’ve strived to uphold in the last three. It is not always easy, but I think you’ll be pleased with how we’ve balanced these two requirements. (ISC) 2 does a really good job of grounding the CISSP Common Body of Knowledge (CBK) in real-world applications, but (let’s face it) there’s always a lot of room for discussion and disagreements. There are very few topics in cybersecurity (or pretty much any other field) on which there is universal agreement. To balance the content of this book between exam preparation and the murkiness of real-world applications, we’ve included plenty of comments and examples drawn from our experiences. I say “our experiences” deliberately because the voice of Shon remains vibrant, infor - mative, and entertaining in this edition, years after her passing. I’ve preserved as many of her insights as possible while ensuring the content is up to date and relevant. I also strove to maintain the conversational tone that was such a hallmark of her work. The result is a book that (I hope) reads more like an essay (or even a story) than a textbook but is grounded in good pedagogy. It should be easy to read but still prepare you for the exam. Speaking of the exam, the changes that (ISC) 2 made to the CBK in 2021 are not dramatic but are still significant. Each domain was tweaked in some way, and seven of the eight domains had multiple topics added (domain 1 was the exception here). These changes, coupled with the number of topics that were growing stale in the eighth edition of this book, prompted me to completely restructure this edition. I tore each domain and topic down to atomic particles and then re-engineered the entire book to integrate the new objectives, which are listed in Table 1. Table 1 CBK 2021: New Objectives ( continued ) Domain 2: Asset Security 2.4 Manage data lifecycle 2.4.1 Data roles (i.e., owners, controllers, custodians, processors, users/subjects) 2.4.3 Data location 2.4.4 Data maintenance 2.5 Ensure appropriate asset retention (e.g., End-of-Life (EOL), End-of-Support (EOS)) Domain 3: Security Architecture and Engineering (Under 3.7 Understand methods of cryptanalytic attacks) 3.7.1 Brute force 3.7.4 Frequency analysis
1330 more pages in the full document
Unlock it once and it stays in your library, ready to chat with or turn into flashcards.
Unlock the full documentMore Certified Information Systems Security Professional study materials
See all Certification Guides
CISSP Cert Guide (2022)
Certified Information Systems Security Professional
1033 pages148downloadsFeb 2025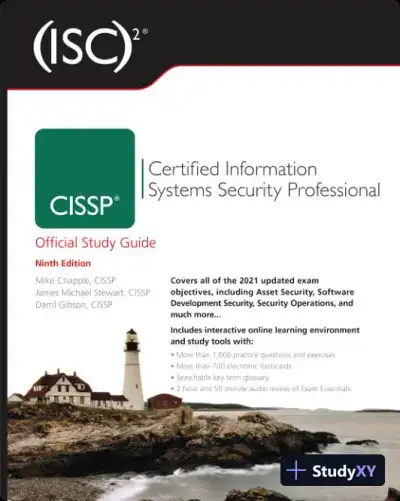 Certification Guides
CISSP Official Study Guide (2021)
Certified Information Systems Security Professional
1250 pages143downloadsFeb 2025 Certification Guides
All in One CISSP Exam Guide (2022)
Certified Information Systems Security Professional
1361 pages143downloadsFeb 2025 Certification Guides
CISSP Official Practice Tests (2021)
Certified Information Systems Security Professional
499 pages109downloadsFeb 2025 Certification Guides
ISC2 Cissp Certified Information Systems Security Professional Official Practice Tests (2021)
Certified Information Systems Security Professional
744 pages109downloadsFeb 2025 Certification Guides
CISSP® Study Guide (2023)
Certified Information Systems Security Professional
642 pages56downloadsFeb 2025 Certification Guides
The Official ISC2 CISSP CBK Reference (2021)
Certified Information Systems Security Professional
674 pages53downloadsFeb 2025 Certification Guides
CISSP Exam Cram, 5th Edition (2021)
Certified Information Systems Security Professional
754 pages45downloadsFeb 2025
Study this document with CramX
Once it is in your library, every tool can work from it.